What Is ISO/IEC 27001?
ISO/IEC 27001 is an international standard for Information Security Management Systems (ISMS). It helps organizations identify information security risks, protect sensitive information, and establish processes to maintain confidentiality, integrity, and availability.
MMK IT Consulting offers ISO/IEC 27001 training options for professionals who want to build their knowledge and develop skills in information security management, implementation, and auditing.
Why is ISO/IEC 27001 important?
ISO/IEC 27001 assists you to understand the practical approaches that are involved in the implementation of an Information Security Management System that preserves the confidentiality, integrity, and availability of information by applying a risk management process. Therefore, implementation of an information security management system that complies with all requirements of ISO/IEC 27001 enables your organizations to assess and treat information security risks that they face.
Certified ISO/IEC 27001 individuals will prove that they possess the necessary expertise to support organizations implement information security policies and procedures tailored to the organization’s needs and promote continual improvement of the management system and organizations operations.
Moreover, you will be able to demonstrate that you have the necessary skills to support the process of integrating the information security management system into the organization’s processes and ensure that the intended outcomes are achieved.
ISO/IEC 27001 Requirements and Controls?
Key Requirements of ISO/IEC 27001
ISO/IEC 27001 outlines several mandatory requirements that ensure a systematic approach to managing sensitive
information. The most important requirements include:
- Context of the Organization
- Identify internal and external issues affecting information security.
- Determine the needs and expectations of stakeholders.
- Leadership and Commitment
- Top management must demonstrate active involvement in ISMS implementation.
- Establish clear roles, responsibilities, and policies
- Risk Assessment and Risk Treatment
- Identify, analyze, and evaluate risks to information security.
- Implement appropriate risk treatments to mitigate identified risks.
- Support
- Provide adequate resources, training, and communication to ensure ISMS effectiveness.
- Operation
- Plan, implement, and control ISMS processes.
- Manage risks and security incidents effectively.
- Performance Evaluation
- Conduct internal audits and management reviews to evaluate ISMS performance.
- Continual Improvement
- Continually improve ISMS effectiveness by addressing nonconformities and implementing corrective actions.
ISO/IEC 27001 Annex A Controls
ISO/IEC 27001 was updated in 2022 to ensure that information security management systems based on it effectively address the ever-evolving security challenges. The revision mainly focused on Annex A, where its controls were restructured into four themes, and the number was reduced from 114 to 93 controls.
The four themes of the security controls of ISO/IEC 27001:2022 are:
Organizational Controls
Policies, responsibilities, risk management, and information security incident management.
People Controls
Employee awareness, training, responsibilities, and personnel-related security measures.
Physical Controls
Protection of facilities, equipment, and physical access to information assets.
Technological Controls
Technical safeguards such as access control, authentication, and cryptography.
The main changes between ISO/IEC 27001:2013 and ISO/IEC 27001:2022
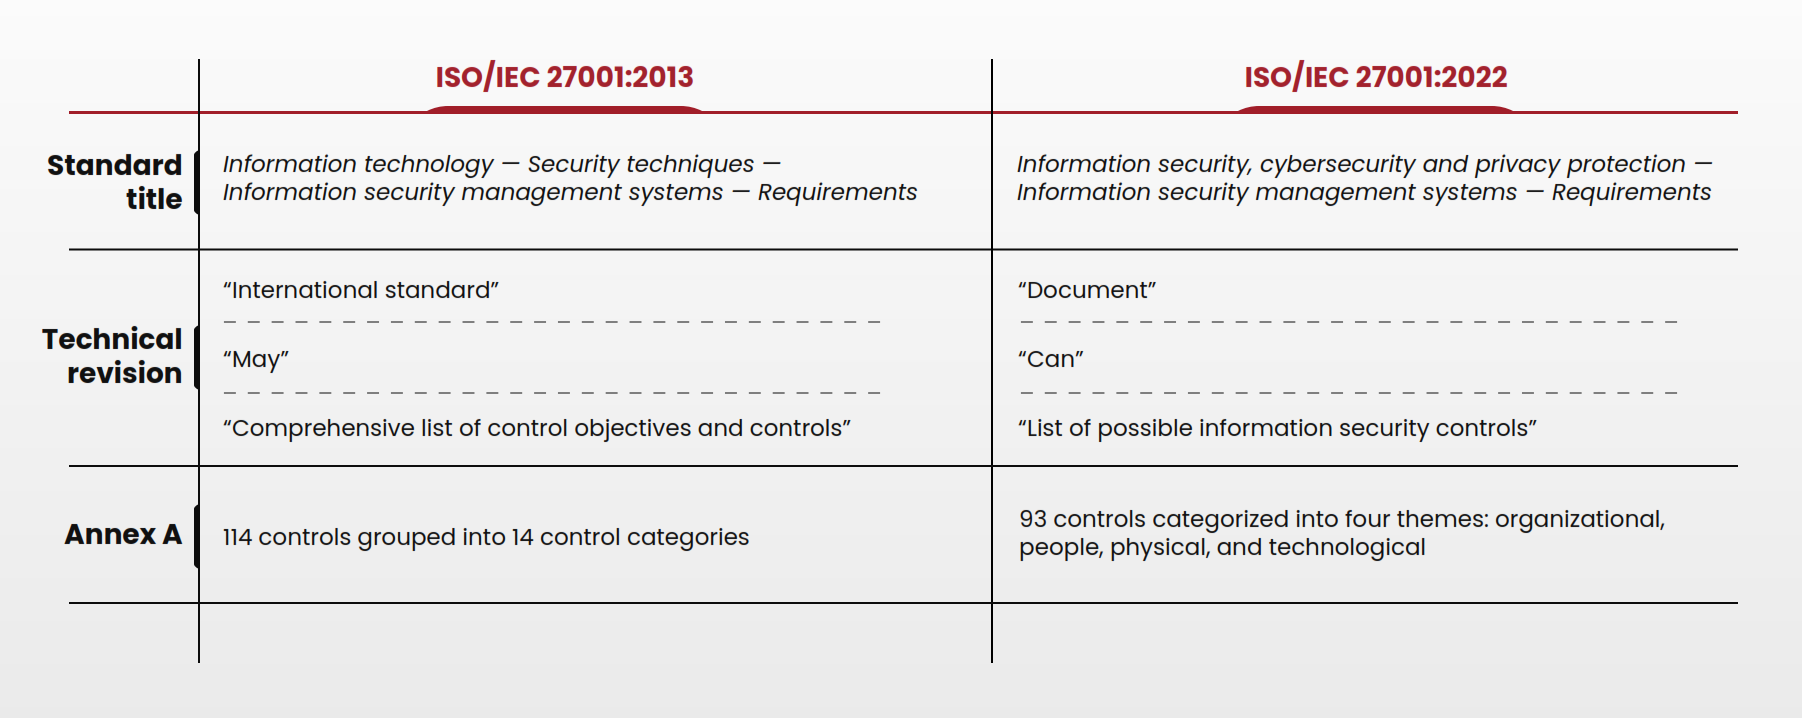
The transition from ISO/IEC 27001:2013 to ISO/IEC 27001:2022 introduces significant updates to align with evolving cybersecurity and privacy needs. The standard title has expanded from focusing solely on “information security management systems” to incorporating “information security, cybersecurity, and privacy protection” in the 2022 version. Technical revisions include replacing terms such as “international standard” with “document” and “may” with “can,” reflecting a more flexible and modern approach.
Additionally, Annex A has been streamlined, reducing the controls from 114 across 14 categories in the 2013 version to 93 controls organized into four key themes: organizational, people, physical, and technological. These changes make the 2022 standard more concise and practical for today’s information security challenges.
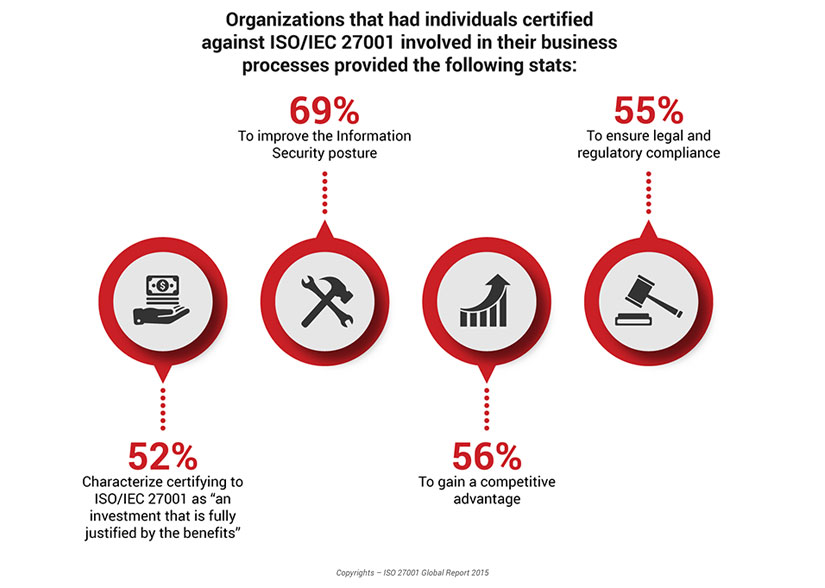
Benefits of ISO/IEC 27001 Certification
Obtaining the PECB ISO/IEC 27001 Certificate will prove that you have:
- Obtained the necessary expertise to support an organization to implement an Information Security Management System that complies with ISO/IEC 27001
- Understood the Information Security Management System implementation process
- Provide continual prevention and assessments of threats within your organization
- Higher chances of being distinguished or hired in an Information Security career
- Understood the risk management process, controls, and compliance obligations
- Acquired the necessary expertise to manage a team to implement an ISMS
- The ability to support organizations in the continual improvement process of their Information Security Management System
- Gained the necessary skills to audit organization’s Information Security Management System
PECB Certified ISO/IEC 27001 training courses available
Learn more about the Information Security Management System through attending the PECB ISO/IEC 27001 training courses. By clicking in one of the options below, you can find the training that best suits to you and your career.
Frequently Asked Questions
Have Questions? Contact Us
5900 Balcones Drive, Suite 100
Austin, TX 78731
United States